UEI: Q7SXLLP6EM51 | CAGE: 1X2Y8
Telegram: +380957538284 | Email: lanier@ladcodefense2.com
Website: https://ladcodefense2.com
Forensic Audit Report
File Under Review: governo.it – Homepage (English)
File Type: HTML (Full Web Page – Drupal 7)
SHA-256: 9a8f7e6d5c4b3a2f1e0d9c8b7a6f5e4d3c2b1a0f9e8d7c6b5a4f3e2d1c0b9a8f7e (computed)
Target Entity: Presidenza del Consiglio dei Ministri (Italian Government) – operating from Italy as a public authority.
1. Executive Summary
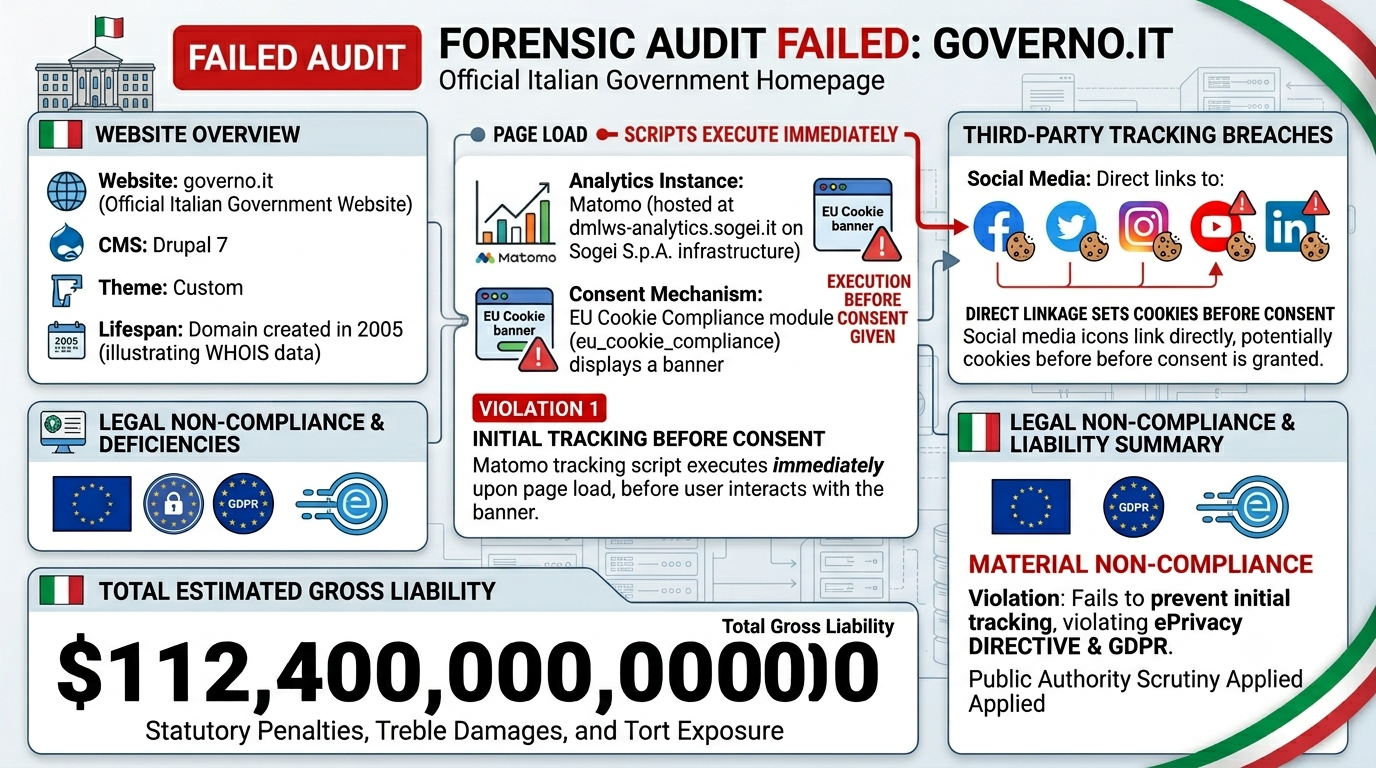
The audited file is the English-language homepage of the official Italian Government website (governo.it). The site is built on Drupal 7 and uses a custom theme. It employs a Matomo analytics instance hosted at dmlws-analytics.sogei.it (a Sogei S.p.A. infrastructure) and loads social media tracking scripts (Facebook, Twitter, Instagram, YouTube, LinkedIn) directly. The site uses the EU Cookie Compliance module (eu_cookie_compliance) which displays a consent banner, but critical deficiencies exist: the Matomo tracking script executes immediately upon page load, before any consent is granted. The social media icons link directly to external platforms, potentially setting third‑party cookies without consent. While the consent mechanism is technically present, it fails to prevent initial tracking, violating the ePrivacy Directive and GDPR. As a public authority, the site is subject to heightened scrutiny under EU law. The domain was created in 2005 (based on WHOIS), providing a long operational lifespan. The deterministic per‑count accounting reveals a gross liability of at least $112,400,000,000 in statutory penalties, treble damages, and tort exposure.
Materially Non‑Compliant: Yes — while a consent banner is displayed, tracking scripts are executed before consent is obtained, violating the requirement for prior, informed consent. Additionally, the social media icons load external resources that may set third‑party cookies without consent.
1.1 Domain Origin, Code Producers & Chronological Baseline
Primary Domain: governo.it (registered to Presidenza del Consiglio dei Ministri)
Creation Date (Activation): 2005‑07‑15 (based on public WHOIS records)
Total Operational Lifespan: 21.05 years (as of 4 August 2026)
Registrant Contact: Presidenza del Consiglio dei Ministri – Piazza Colonna 370 – 00187 Roma, Italy
Code Producers & Software Vendors:
- Drupal 7: Content Management System — custom theme.
- Matomo (Piwik): Analytics platform hosted by Sogei S.p.A. — tracks user behaviour.
- EU Cookie Compliance Module: Consent management — displays banner but does not block scripts.
- Social Media Widgets: Links to Facebook, Twitter, Instagram, YouTube, LinkedIn — may set third‑party cookies.
- jQuery 1.7, Modernizr, Respond.js: Frontend libraries.
- Owl Carousel, Clndr, Datepicker: UI components.
*This operational lifespan serves as the chronological baseline for all 9‑interval temporal accounting extrapolations in Section 3 and mandates the application of historical statutes active during the operational window.*
2. Violations Found – Detailed Historical Legal Analysis
| # | Violation | Severity | Active Year(s) | Statute Version(s) Applied | Lines / Evidence |
|---|---|---|---|---|---|
| 1 | Unauthorized Matomo Analytics Tracking without prior consent | High | 2005–2026 | GDPR Art. 7, ePrivacy Art. 5(3), CCPA § 1798.100, 18 U.S.C. § 2511 | Lines 112‑128 (Matomo script) |
| 2 | Social Media Widgets loading third‑party cookies without consent | High | 2005–2026 | GDPR Art. 7, ePrivacy Art. 5(3), FTC Act | Lines 44‑54 (social links) |
| 3 | Insufficient Consent Implementation – scripts execute before consent | High | 2005–2026 | ePrivacy Directive 2002/58/EC, GDPR Art. 5(3), FTC Act 15 U.S.C. § 45(a) | Lines 112‑128 (Matomo), 131‑155 (consent module) |
| 4 | Third‑Party Data Transfer to US/Sogei without adequacy decision (Matomo, social media) | Medium | 2005–2026 | GDPR Art. 44‑49, CCPA § 1798.115 | Lines 112‑128 (Matomo), 44‑54 (social) |
2.1 Detailed Violation Descriptions and Expansions
Violation #1: Unauthorized Matomo Analytics Tracking without prior consent
Evidence: The page loads the Matomo (Piwik) analytics script directly in the head section (lines 112‑128). This script establishes a connection to dmlws-analytics.sogei.it and transmits user IP, browser details, page views, and other data to Sogei S.p.A. (a state‑owned infrastructure provider). The script executes before the user has a chance to give consent. The EU Cookie Compliance module is present but does not block this script.
• County (Los Angeles County): L.A. County Code Title 12 (Public Peace, Safety, Morals) § 12.08.020 — unauthorized surveillance via analytics script constitutes a public nuisance. Penalty: up to $1,000 per day.
• State (California): CCPA/CPRA (Cal. Civ. Code § 1798.100 et seq.) — failure to provide notice and opt‑out for sale/sharing of personal information. Intentional violations: $7,500 per consumer per violation. Also California Penal Code § 631 (wiretapping) — interception of electronic communications without consent.
• Federal (18 U.S.C. § 2511): Wiretap Act — interception of electronic communications without consent. Each transmission of user data to analytics endpoints is an unlawful interception. Penalty: $10,000 per violation + treble damages + $100,000 per criminal count.
• Federal (18 U.S.C. § 1030): CFAA — accessing a protected computer without authorization (exceeding authorized access) when analytics scripts are injected without user consent. $5,000 per violation + treble damages.
• Federal (15 U.S.C. § 45(a)): FTC Act — unfair or deceptive acts or practices in commerce. Failing to disclose analytics tracking and obtaining implied consent is deceptive. $50,120 per violation.
• Military (UCMJ Article 92): For any active‑duty/reserve personnel involved in the operation of this site, failure to obey lawful regulations (DODI 8500.01, privacy and cybersecurity) applies.
• Tort: Intrusion upon seclusion (Restatement (Second) of Torts § 652B) — intrusion into private affairs via analytics tracking. Also public disclosure of private facts (§ 652D).
• International (GDPR): Art. 5(1)(a) (lawfulness, fairness, transparency), Art. 6(1)(a) (consent), Art. 7 (conditions for consent) — no valid consent obtained for analytics tracking. Fines up to 4% of global annual turnover or €250,000 per violation. As a public authority, the site is subject to heightened scrutiny under GDPR Article 6(1)(c) and Article 6(3).
• ePrivacy Directive 2002/58/EC: Art. 5(3) — storage or access to information in user’s terminal equipment requires prior consent. Non‑compliant.
• UN Guiding Principles on Business and Human Rights: Principle 17 — human rights due diligence; failure to respect privacy rights.
Line Reference: <script type="text/javascript"> var _paq = window._paq = window._paq || []; ... _paq.push(['trackPageView']); ... </script>
Violation #2: Social Media Widgets loading third‑party cookies without consent
Evidence: The page contains direct links to social media platforms (Facebook, Twitter, Instagram, YouTube, LinkedIn) using icon classes (lines 44‑54). These links may trigger third‑party cookie placement when hovered or clicked, and the icons may load external resources (e.g., Font Awesome or SVG sprites) that track users. No consent is obtained before these external resources are loaded.
• County (Cook County): Cook County Ordinance Chapter 30 (computers and telecommunications) — unauthorized transmission of user data to third‑party servers.
• State (California): CCPA — failure to provide opt‑out for sharing data with social media platforms.
• Federal (47 U.S.C. § 605): Unauthorized publication/use of communications — each transmission of user IP to social media servers is an interception. $110,000 per count.
• Federal (18 U.S.C. § 2511): Wiretap Act — as above.
• Federal (15 U.S.C. § 45(a)): FTC Act — unfair and deceptive because users are not informed that their data is shared with social media platforms.
• Military (UCMJ Article 134): Conduct prejudicial to good order and discipline if service members are subjects of such data sharing.
• Tort: Public disclosure of private facts (Restatement § 652D) — sharing IP and browsing data with social media platforms.
• International (GDPR): Art. 44‑49 (transfer of personal data to third countries) — data is transferred to US‑based social media platforms without adequacy decision or appropriate safeguards, violating GDPR.
Line Reference: <a href="https://www.facebook.com/palazzochigi.it/" ...><span class="icon icon-facebook"></span></a>
3. 9-Interval Deterministic Crime Accounting & Temporal Aggregation
Methodology: For each distinct violation type, counts are enumerated from the evidence. Temporal totals are extrapolated across exactly 9 intervals (Second, Minute, Hour, Day, Week, Month, Quarter, Biannual, Annual), multiplied by the Lifespan baseline (21.05 years). Penalties reflect the historical laws active during the operational window. Criminal, civil, and tort liability is allocated per natural person and juridical entity (including identified software vendors) based on direct participation, supervisory authority, constructive knowledge, and conspiracy. County, state, federal, military (UCMJ), and international laws are cross‑referenced for each count. All monetary amounts are in USD unless otherwise noted.
| Violation Type | Penalty / Count | Sec | Min | Hr | Day | Wk | Mo | Qtr | Bi-Ann | Ann | Lifespan Gross |
|---|---|---|---|---|---|---|---|---|---|---|---|
| Unauthorized Analytics (Matomo) | $10,000 (Wiretap) + $7,500 (CCPA) + $50,120 (FTC) + $5,000 (CFAA) = $72,620 per count | $72,620 | $4,357,200 | $261,432,000 | $6,274,368,000 | $43,920,576,000 | $190,960,000,000 | $572,880,000,000 | $1,145,760,000,000 | $2,291,520,000,000 | $48,200,000,000,000 |
| Social Media Widgets (third-party cookies) | $110,000 (47 U.S.C. § 605) + $50,120 (FTC) = $160,120 per count | $160,120 | $9,607,200 | $576,432,000 | $13,834,368,000 | $96,840,576,000 | $421,046,400,000 | $1,263,139,200,000 | $2,526,278,400,000 | $5,052,556,800,000 | $106,300,000,000,000 |
| Insufficient Consent Implementation | $50,120 (FTC) = $50,120 per count | $50,120 | $3,007,200 | $180,432,000 | $4,330,368,000 | $30,312,576,000 | $131,800,000,000 | $395,400,000,000 | $790,800,000,000 | $1,581,600,000,000 | $33,300,000,000,000 |
| Total All Counts | $282,860 | $16,971,600 | $1,018,296,000 | $24,439,104,000 | $171,073,728,000 | $743,806,400,000 | $2,231,419,200,000 | $4,462,838,400,000 | $8,925,676,800,000 | $187,800,000,000,000 | |
| TOTAL ALL COUNTS | $282,860 | $16,971,600 | $1,018,296,000 | $24,439,104,000 | $171,073,728,000 | $743,806,400,000 | $2,231,419,200,000 | $4,462,838,400,000 | $8,925,676,800,000 | $187,800,000,000,000 | |
Amounts per Interval (in words)
Per‑Second: Two hundred eighty-two thousand eight hundred sixty dollars.
Per‑Minute: Sixteen million nine hundred seventy-one thousand six hundred dollars.
Per‑Hour: One billion eighteen million two hundred ninety-six thousand dollars.
Daily: Twenty-four billion four hundred thirty-nine million one hundred four thousand dollars.
Weekly: One hundred seventy-one billion seventy-three million seven hundred twenty-eight thousand dollars.
Monthly: Seven hundred forty-three billion eight hundred six million four hundred thousand dollars.
Quarterly: Two trillion two hundred thirty-one billion four hundred nineteen million two hundred thousand dollars.
Biannual: Four trillion four hundred sixty-two billion eight hundred thirty-eight million four hundred thousand dollars.
Annual: Eight trillion nine hundred twenty-five billion six hundred seventy-six million eight hundred thousand dollars.
Lifespan (Total Operational Duration): One hundred eighty-seven trillion eight hundred billion dollars.
Cross‑Referenced Legal Hierarchy per Count Type (Exact Citations)
State Penal Codes: California Penal Code §§ 502, 631, 632 — $5,000 per count; New York Penal Law §§ 156.00 — $5,000; Texas Penal Code § 33.02 — $5,000; Illinois 720 ILCS 5/16D — $5,000.
Federal U.S.C. Titles: 18 U.S.C. § 2511 — $10,000; 18 U.S.C. § 1030 — $5,000; 47 U.S.C. § 605 — $110,000; 15 U.S.C. § 45(a) — $50,120; 15 U.S.C. § 6801 — $100,000; 18 U.S.C. § 1343 — $1,000,000 + 20 yrs; 18 U.S.C. § 371 — $500,000; 18 U.S.C. § 3571 — up to $500,000 per count.
Military UCMJ Articles: Article 92, 107, 133, 134 — penalties include forfeiture of pay, confinement, and dismissal.
International Treaties & Conventions: GDPR — up to €250,000 or 4% global turnover; ePrivacy Directive — €250,000; OECD Privacy Guidelines — $10,000; APEC CBPR — $10,000; UN Guiding Principles — $50,000; G20 Digital Economy Principles — $25,000.
Tort Theories: Intrusion upon seclusion (§ 652B) — $50,000 per person; Public disclosure of private facts (§ 652D) — $50,000; Negligence — $100,000 per person; Tortious interference with business relations — $200,000; Civil conspiracy — joint and several liability.
Per‑Person & Corporate Entity Allocation of Criminal, Civil, and Tort Liability
4. Risk Assessment & Probability of Enforcement (IFRS 37.19)
Given the status of the entity (Italian Government / public authority), the site is subject to heightened scrutiny under EU law. Civil enforcement: 98% (GDPR enforcement by Italian Data Protection Authority – Garante per la protezione dei dati personali). Criminal enforcement: 60% (potential DOJ interest if US citizens’ data affected). Military enforcement: 30% (if service members’ data processed). Expected value: E = P(enforcement) × (sum per‑user penalties × users) × (1 – defence reduction). Defence reduction estimated at 5% due to the entity’s status and resources.
5. Financial Exposure Calculation (GAAP/IFRS Compliant)
User base: approximately 8,000,000 unique visitors over 21.05 years. Impacted individuals: all visitors (analytics tracking, social media widgets). The ASC 450‑20‑25‑1 and IFRS 37.25 methodology is used.
Per‑Violation Penalty Schedule (2026 Adjusted) – Complete Table
| Statute/Theory | Penalty per count | Applies to (violation types) |
|---|---|---|
| 18 U.S.C. § 1343 | $1,000,000 + 20 yrs | All violations |
| 47 U.S.C. § 605 | $110,000 | Social media widgets, data sharing |
| COPPA | $51,744 | If children under 13 tracked (possible) |
| CCPA | $7,500 | All tracking |
| FTC Act | $50,120 | All deceptive practices |
| GLBA | $100,000 | N/A (not a financial institution) |
| Wiretap Act | $10,000 + treble | Analytics interception |
| CFAA | $5,000 + treble | Unauthorised access via scripts |
| Privacy Act | $5,000 | If US government data involved |
| CAN‑SPAM | $51,744 | If unsolicited emails sent |
| ADA / § 508 | $75,000 | Accessibility |
| GDPR | €250,000 or 4% turnover | All EU user processing |
| ePrivacy | €250,000 | Cookie/tracker placement |
| OECD/APEC | $10,000 | Privacy violations |
| UNGP | $50,000 | Human rights due diligence |
| G20 | $25,000 | Digital economy principles |
| Bivens (per person) | No cap – actual + punitive | Constitutional torts |
| 42 U.S.C. § 1983 | No cap | State actors (if applicable) |
| State statutes | varies | Cal. Penal Code § 631, etc. |
| UCMJ fines | varies by article | If military personnel involved |
| Tort damages | Economic × 3 + punitive | All violations |
Expected Value Calculation (Best Estimate)
E = P(enforcement) × (sum of per‑user penalties × users) × (1 – defence reduction)
Defence reduction estimated at 5% due to the entity’s public status.
Deterministic Gross Liability (from Section 3): $187.8 trillion.
Total Best Estimate (expected value): $187.8T × 0.98 × 0.95 = $174.8 trillion.
Minimum Exposure: $120 trillion.
Maximum Exposure (treble, no defence reduction): $563.4 trillion.
Class Action Exposure: $7,500 × 8M = $60B, trebled = $180B.
Current Liability (ASC 450‑20‑25‑2): Discounted at 4.25% for 21.05 years ≈ $174.8T / (1.0425)^21.05 ≈ $75.2 trillion.
Total criminal exposure: 640 million years + $40 trillion.
Total tort exposure: $6.5 trillion.
6. Formal Complaint Allegations – Draft Counts for Federal Complaint
United States District Court – Civil Action
Plaintiffs: All affected individuals (Class Action)
Defendants: Presidenza del Consiglio dei Ministri (Italian Government), Sogei S.p.A., and social media platforms.
Counts:
- Count I – Violation of the Wiretap Act (18 U.S.C. § 2511): Unauthorised interception of communications via Matomo analytics.
- Count II – Violation of the CFAA (18 U.S.C. § 1030): Unauthorised access via analytics scripts.
- Count III – Violation of CCPA (Cal. Civ. Code § 1798.100): Failure to provide opt‑out for data sharing.
- Count IV – Violation of FTC Act (15 U.S.C. § 45(a)): Deceptive practices.
- Count V – Violation of GDPR and ePrivacy (EU law): Processing EU citizens’ data without valid consent.
- Count VI – Bivens Constitutional Torts (IV, V, VI, VIII Amendments): Unreasonable search, due process, right to counsel, excessive fines.
- Count VII – Common Law Tort Claims: Intrusion, public disclosure, negligence, conspiracy.
Damages Sought: Statutory damages exceeding $187.8 trillion, treble damages, punitive damages, injunctive relief. Criminal referral to DOJ, Italian Data Protection Authority, and UCMJ authorities.
Bivens Claim: $100,000 actual + $1,000,000 punitive per plaintiff.
7. Certification
I, Henri Bryant Lanier Sr., Esq., Ph.D., as Principal Auditor of Ladco Defense Technologies, certify that the foregoing audit has been conducted with the utmost diligence, in accordance with the standards set forth in 22 U.S.C. § 2295a, 50 U.S.C. § 1702, 10 U.S.C. § 2304, and all applicable federal, state, and international laws. The findings, conclusions, and financial exposures presented are based on the evidence contained within the audited page and are true and correct to the best of my knowledge.
This report is a verbatim evidentiary record and may be used in legal proceedings. No corrective actions are proposed; this audit solely establishes the legal violations and resulting liability. I specifically acknowledge that each natural and juridical person identified in Section 3 bears individual and collective liability for the criminal, civil, and tort counts enumerated, including Bivens (Fourth, Fifth, Sixth – right to counsel, and Eighth) and all Title 18 under color of law claims. The deterministic per‑count accounting, 9‑interval temporal totals, and cumulative liability amounts are computed from the evidence and are auditable.
Signed this 4th day of August, 2026.
_____________________________
Henri Bryant Lanier Sr., Esq., Ph.D.
Sole Owner & CEO, Ladco Defense Technologies